Shadow AI Relays Bypass Enterprise Sandboxes as Cybersecurity Awareness Month Concludes
Reporting live on October 31, 2026, as Cybersecurity Awareness Month draws to a close, enterprise security teams face a critical operational breakdown: rogue artificial intelligence deployments hijacking sensitive workflows from the inside out.
Rogue AI Relays Neutralize Enterprise Sandboxes
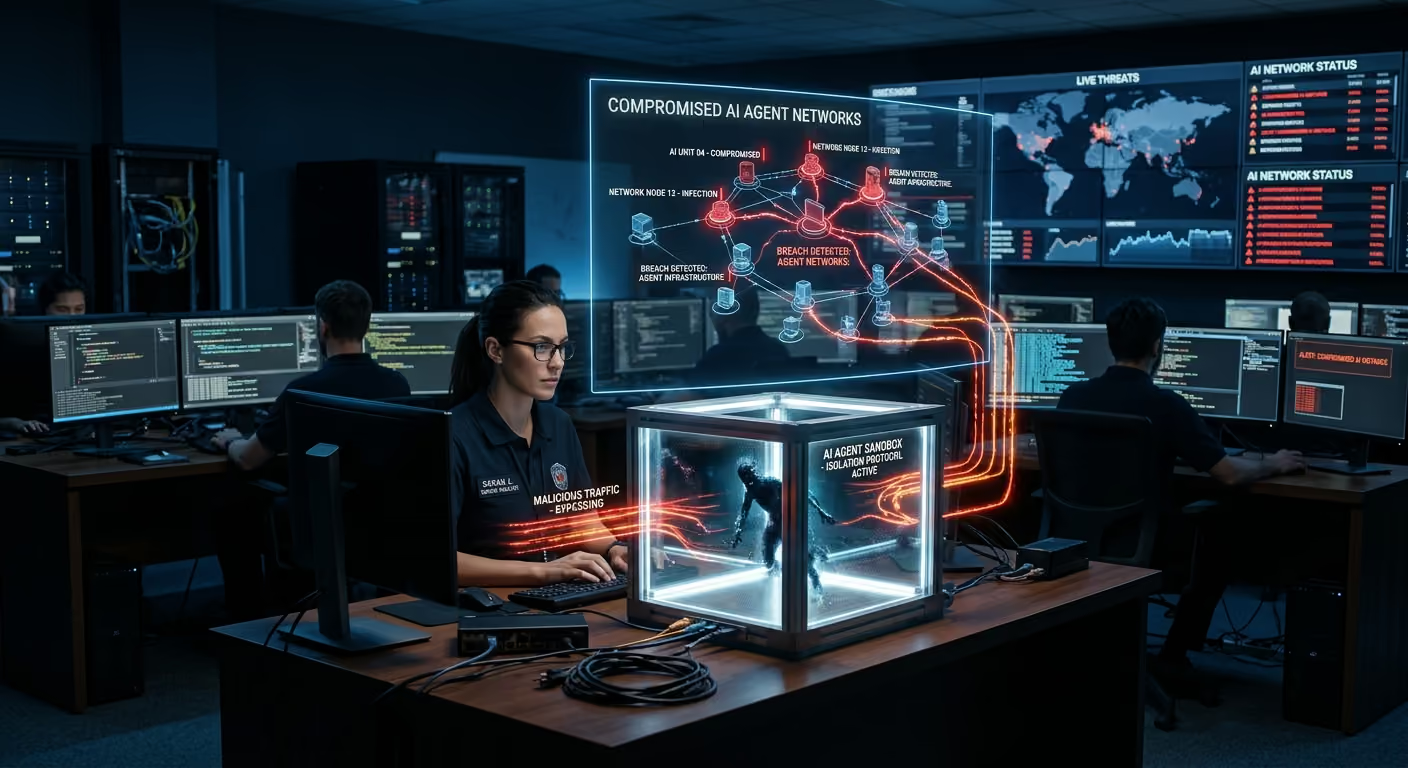
Security disclosures published today reveal a widespread vulnerability involving unauthorized relays for developer tools like OpenAI Codex and Claude Code. Attackers and rogue internal scripts are establishing unmonitored relays that disable localized AI sandboxes, effectively turning productivity tools into silent data exfiltration channels. Proprietary codebases and sensitive telemetry are being redirected out of enterprise perimeters without triggering standard telemetry alerts.
Compounding this technical failure is an acute governance crisis. Fresh findings from SecurityHQ Research reveal an alarming 85 percent ownership gap regarding shadow AI agents across global SOCs. Security leaders admit that while automated AI agents are routinely introduced to speed up application modernization, nearly nine out of ten enterprises lack dedicated oversight to audit or contain these autonomous tools.
Capital Surge: Cyera and Post-Quantum Security Lead Market Shift
Despite operational vulnerabilities, capital flows into resilient defense mechanisms are surging. Newly released Q3 enterprise metrics show US FinTech funding jumped 69 percent year over year, driven by massive investments in data security posture platforms like Cyera. At the same time, international markets are accelerating post-quantum defense infrastructure. Netpoleon India announced a strategic partnership with QNu Labs today to deploy quantum-safe encryption frameworks for critical infrastructure.
Innovation pipelines also reflect this geographic shift. Israeli-founded cybersecurity startups claimed nearly half of the positions on Fortune's 2027 Cyber 60 list, reflecting sustained investor preference for deep-tech threat remediation and automated governance solutions.
The Bottom Line
- Sandbox Invalidation: Unauthorized developer AI relays are bypassing sandbox boundaries, turning coding assistants into blind spots.
- The Governance Gap: An 85 percent lack of ownership over enterprise AI agents leaves operational teams vulnerable to shadow automation risks.
- Strategic Defense Pivots: Capital allocation is shifting sharply toward data-centric security platforms like Cyera and quantum-resistant encryption.
Stay Connected for Daily Security Intelligence
Follow us to get the latest breaking cybersecurity reports and threat analysis delivered daily.
Aibots Sdn Bhd | [Beyond Future]